R. Response (recover)
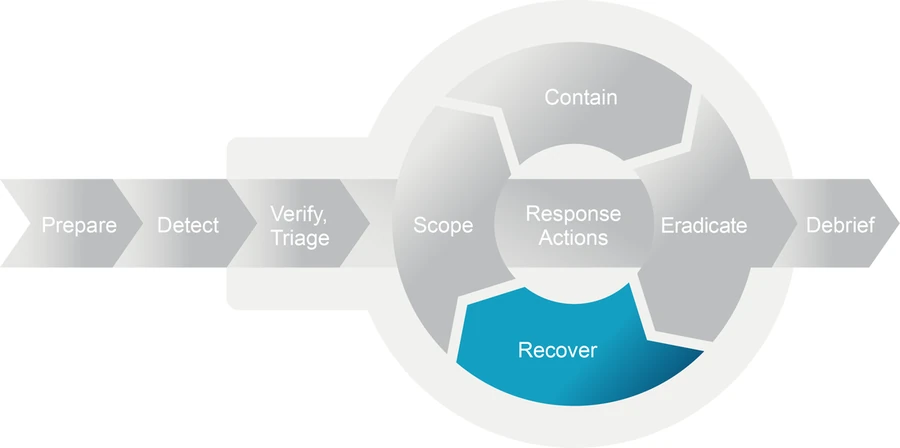
STARTS WHENEradication verified.
DONE WHENSystems in production under enhanced monitoring, owner sign-off on file.
Work the checks in order before anything returns to production. The indicator scan comes last, because scanning a half-patched box tells you nothing about the build that ships.
Pre-restoration verification
| # | Item |
|---|---|
| 1 | Root cause remediated. Vulnerability patched, credentials rotated, or misconfiguration corrected, matched to the root cause analysis. |
| 2 | Patching current. Operating system, firmware, and application updates missed while offline. |
| 3 | Persistence removed. Every identified mechanism confirmed gone. |
| 4 | Backup validated. For restores, the backup predates initial compromise according to the incident timeline. |
| 5 | Rebuild verified. For rebuilds, trusted sources and clean installation media. |
| 6 | Controls live. EDR installed and reporting, host firewall configured, logging enabled. |
| 7 | Indicator scan, last. Every indicator from scoping and eradication, against the final build. |
Then the rest
| # | Item |
|---|---|
| 8 | Validation testing performed against a written test plan |
| 9 | System owner acceptance recorded: what was tested, by whom, limitations accepted, formal sign-off |
| 10 | Enhanced monitoring configured before go-live: advanced audit policies, PowerShell script block logging on Windows, auditd rules on Linux, logs confirmed flowing to the SIEM |
| 11 | Detection rules written during contain and eradicate enabled on the restored system |
| 12 | Production restoration coordinated across teams |
| 13 | Containment measures removed deliberately, each one decided rather than left in place |
| 14 | Recovery metrics captured for the debrief |